The PII Firewall: A Clever Idea With a Blind Spot
By Het Schrijfhuis
---
At some point in the past year, most knowledge workers have done it: pasted a contract, a medical record, or a client email into ChatGPT or Claude, knowing they probably shouldn't. The convenience won out over the caution. Now a new category of tools is trying to eliminate that tradeoff — and the story of how they work reveals something important about what "AI privacy" actually means in practice.
Adrianus Warmenhoven and Reza Rafati know the feeling well. Both Dutch cybersecurity veterans — Warmenhoven holds ten US patents in network security and spent years as CISO at Dutch firm Tesorion; Rafati founded Cyberwarzone in 2010 and led threat intelligence operations at Group-IB across Europe — they kept running into the same problem when they tried to use AI for actual work. Every tool sent data to a cloud server. API keys sat in plaintext files. Nothing was auditable. The tools that promised to be helpful were, from a security standpoint, a mess.
So they built Feluda: a free desktop application, released in 2025, that lets you build AI automation workflows on your own machine. It connects directly to cloud providers like OpenAI, Anthropic, and Mistral — but before any text leaves your computer, Feluda scrubs it. Names, email addresses, phone numbers, financial identifiers: seventeen categories of personal data, stripped automatically and replaced with placeholders. What arrives at the cloud provider is a sanitized version of your question. The original values never leave.
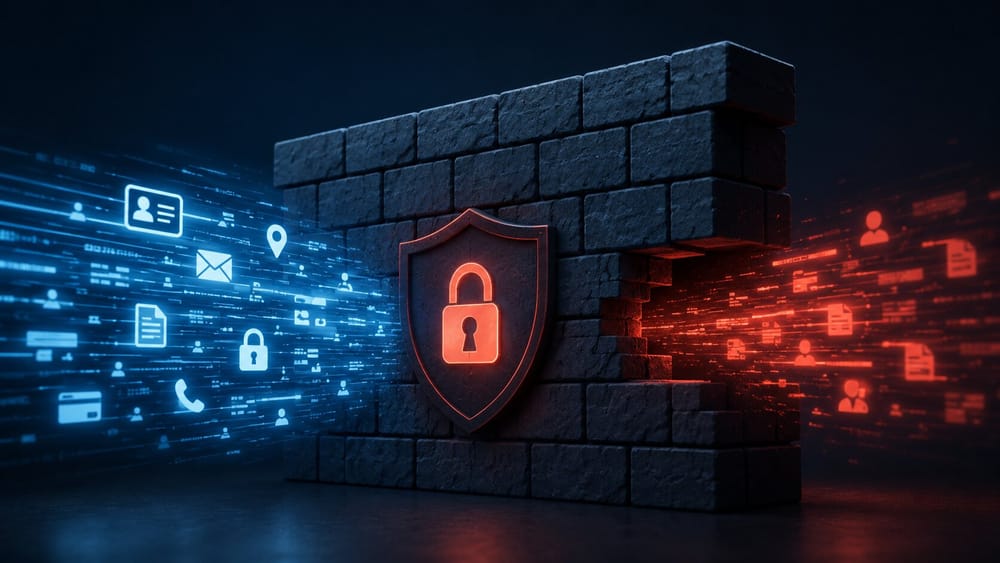
It is a clean idea, and it sits at the center of a pattern that is becoming standard practice in enterprise AI: the PII firewall.
---
How the Scrub Works
The technical mechanism is simpler than it sounds. Tools like Feluda — and its open-source counterparts, Microsoft's Presidio and OpenPipe's pii-redaction library — run a detection pass over your text before it goes anywhere. They use a combination of regular expression matching (find strings that look like phone numbers or credit cards) and named entity recognition, a form of NLP that identifies people, places, and organizations in context.
When the system spots something sensitive, it replaces it with a placeholder token. `Sarah Chen` becomes ``. `sarah.chen@company.com` becomes ``. A context map stores the mapping between placeholders and originals. The scrubbed text goes to the cloud model. The response comes back with the same placeholders intact. Before the user sees anything, the system swaps them back. The LogRocket engineering blog calls this the "scrub-and-rehydrate" pattern — and it is exactly as mechanical as it sounds.
Feluda stores your API keys not in config files but in the operating system's secure vault — the macOS Keychain, Windows Credential Manager, or Linux's equivalent. Every API call goes directly from your machine to the provider. There is no Feluda cloud sitting in the middle, logging traffic. That architectural choice matters: many SaaS AI tools route your prompts through their own servers, which means you're trusting both the AI provider and the SaaS company. Feluda removes one layer of trust.
---
"Local" Has an Asterisk
The phrase "data stays local" appears prominently in Feluda's marketing and in the marketing of every similar product. It deserves scrutiny.
When you run Feluda connected to Ollama — the local model runner that lets you run Llama or Mistral entirely on your own hardware — "local" is completely accurate. No internet connection required, no data leaves the machine, inference runs on your CPU or GPU. In that configuration, Feluda's PII scrubbing adds no privacy benefit: the data was never going anywhere anyway. Feluda's value there is its workflow automation features. The firewall only becomes meaningful when you connect to a cloud provider.
When you use Feluda to query OpenAI or Anthropic, the picture is different. The PII values don't leave your machine — but the text does. The cloud provider sees your question, your context, your reasoning, your document structure. It just doesn't see the names, emails, and phone numbers that have been stripped out. That is meaningfully better than nothing. It is not the same as the data staying local.
OpenAI, interestingly, launched its own contribution to this space in April 2026: Privacy Filter, a 1.5-billion-parameter open-source model (Apache 2.0 license) designed to scrub PII before it reaches any cloud service. It runs on a standard laptop, processes documents up to 128,000 tokens in a single pass, and achieves state-of-the-art results on the PII-Masking-300k benchmark. The market irony is not subtle: OpenAI is now releasing tools specifically designed to prevent data from reaching OpenAI. This publication examined the strategic logic behind that move in The Privacy Paradox — Why OpenAI Is Building An Anti-Cloud Tool.
The Blind Spot
Here is where the pattern runs into its structural limit.
PII stands for personally identifiable information — data that can identify a specific person. The regulatory frameworks that drive PII protection, GDPR in Europe and its equivalents elsewhere, are primarily concerned with individual rights: the right not to have your name, address, or health data mishandled.
But organizations worry about a different category of sensitive data that has nothing to do with individuals. A contract negotiation strategy. A pharmaceutical compound formula. Source code for an unreleased product. Internal pricing decisions. An HR document about a reorganization that hasn't been announced.
None of these are PII. A regex engine or a named entity recognizer will not flag them. They will pass through a PII firewall untouched and arrive at the cloud provider in their original form.
Walk through a common scenario: a legal team asks Claude to help draft a response to a contract dispute. Feluda does its job. The opposing counsel's name becomes ``. The firm's email becomes ``. What leaves the machine intact: the negotiation strategy, every concession on the table, the leverage points, the settlement range the client has authorized. The cloud model sees all of it. The names are gone. The deal is not.
This is not a flaw in Feluda's implementation. It is a fundamental limitation of what PII detection is designed to do. "The model understands it is working with a person's name without ever seeing the actual values," as one enterprise security firm describes the placeholder approach. True. But the model knows exactly what the unnamed contract says, what the undisclosed product does, and what the strategic decision entails.
OWASP, the organization that maintains security best-practice frameworks, elevated Sensitive Information Disclosure to the second position in its 2025 AI Top Ten — precisely because the exposure surface has grown. AI systems require more organizational data to function well, and more data means more potential leakage of things that are sensitive without being personal.
NER models themselves have acknowledged gaps. Research on multilingual PII detection found that standard approaches miss domain-specific identifiers — internal employee IDs, medical room numbers, platform-specific handles — that don't match training patterns. A regex baseline captures roughly 65% of PII in unstructured text, meaning up to 35% slips through even for the data it is designed to catch. For business-sensitive non-PII data, the miss rate is essentially 100%.
---
Where It Fits in the Stack
None of this makes the PII firewall pattern useless. It makes it legible.
For professionals handling consumer data — customer service agents, HR teams, healthcare workers — PII redaction solves a real compliance problem and reduces genuine regulatory risk. GDPR enforcement, which escalated in 2025 under the AI Act provisions, makes this a matter of meaningful legal exposure. Getting that data out of cloud prompts is valuable, and tools like Feluda do it cleanly.
For organizations worried about competitive intelligence, trade secrets, or proprietary processes, PII redaction is one layer in what needs to be a thicker stack. The alternatives range from running fully local models (which sacrifices output quality unless you have serious GPU infrastructure) to enterprise agreements with no-training clauses (which adds contractual protection without changing the technical exposure) to on-premises inference deployments (high cost, high control). PII redaction addresses part of the architecture. The non-PII exposure remains.
Microsoft Presidio, the open-source SDK that has become the reference implementation for the pattern, explicitly acknowledges in its documentation that "automated detection cannot guarantee complete PII identification" — and that is before you even start asking about non-PII confidentiality. Additional protective systems remain necessary.
---
Two Sides of the Same Coin
Earlier this week, this publication covered Anthropic's Mythos — a government AI system operating outside normal oversight channels, its capabilities visible only to cleared officials. That story was about power staying invisible: AI that governments deploy without accountability.
The PII firewall pattern is the mirror image: individuals and organizations trying to keep their data invisible from AI providers. Same underlying tension, opposite vantage point. Who controls what the AI sees?
Warmenhoven and Rafati built Feluda because they believed the answer to that question was ending up in the wrong hands by default. Their tool is a reasonable response to a real problem — and like any security control, its value depends entirely on understanding what it protects against and what it does not.
A firewall is not a bunker. It stops specific traffic. Everything else still gets through.
---
Sources
PII Firewall Tools & Implementations
- Feluda — privacy-first AI automation — Product website; founding story, feature overview, local API key storage architecture
- Microsoft Presidio — open-source PII detection SDK — Reference implementation; documentation on detection limits and "additional protective systems" disclaimer
- OpenPipe pii-redaction library — Open-source PII redaction library for LLM workflows
- Build a local AI proxy to redact PII before it reaches LLMs — LogRocket — Technical walkthrough introducing the "scrub-and-rehydrate" pattern name
OpenAI Privacy Filter
- OpenAI releases Privacy Filter — MarkTechPost — Coverage of the April 2026 Privacy Filter release; 1.5B parameters, Apache 2.0, 128k-token context
- OpenAI Privacy Filter — GitHub — Repository; benchmark results on PII-Masking-300k
Detection Limits & Security Context
- NER models for PII detection in LLM workflows — Protecto — Analysis of named entity recognition gaps; domain-specific identifiers that evade standard models; regex baseline coverage rate
- Preventing LLM data leakage — Kiteworks — Enterprise perspective on PII vs. non-PII confidentiality; OWASP AI Top Ten context